Command filter configuration for SSH and database queries
Command ACL Configuration
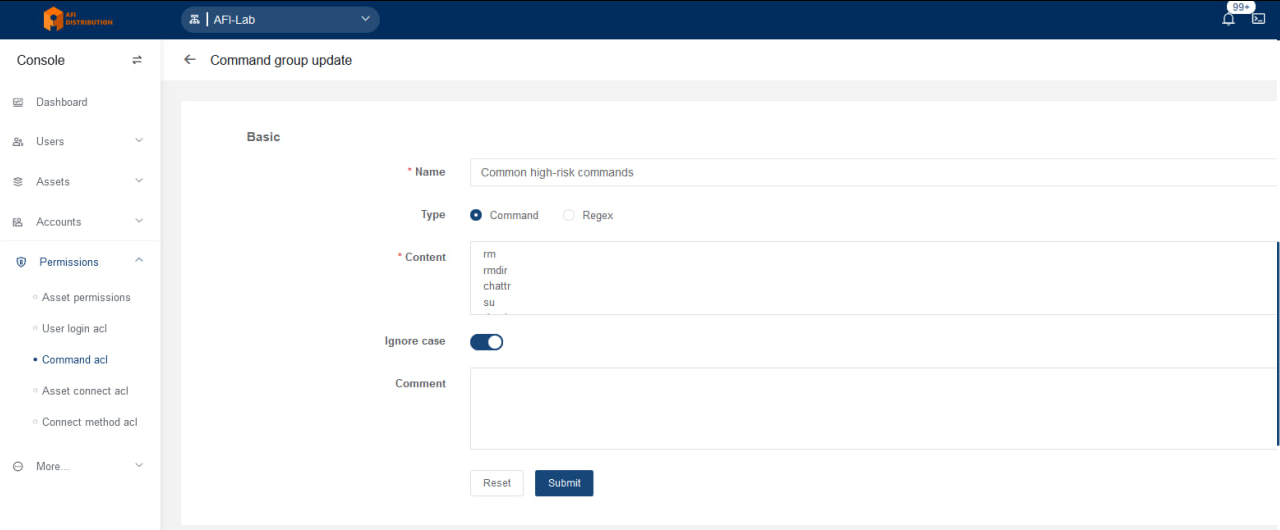
1. Go to the "Console - Policies - ACLs - Command filter" section and open the "Command Group" tab.
2. Click the "Create" button, enter a name for the
list, such as "Common high-risk commands", and
fill in the list with the required commands or regular expressions
(see the screenshot). Save it by clicking the
"Submit" button.
3. Open the "Command filter" tab and click "Create" to create a filter.
4. The filter configuration includes the following parameters:
- Priority: the filter priority. The action of the
filter with the highest priority will always be executed.
- User: JumpServer users for whom the filter will
apply.
- Asset: target systems where the filter will
control connections.
- Account: accounts on target systems that will be
controlled by the filter.
- Command Group: groups of commands that will be
blocked.
- Action: the filter action:
Reject - block the command,
Accept - execute the command,
Review - send the command for approval by a
specified employee, Warning - warn the specified
employee about executing the command.
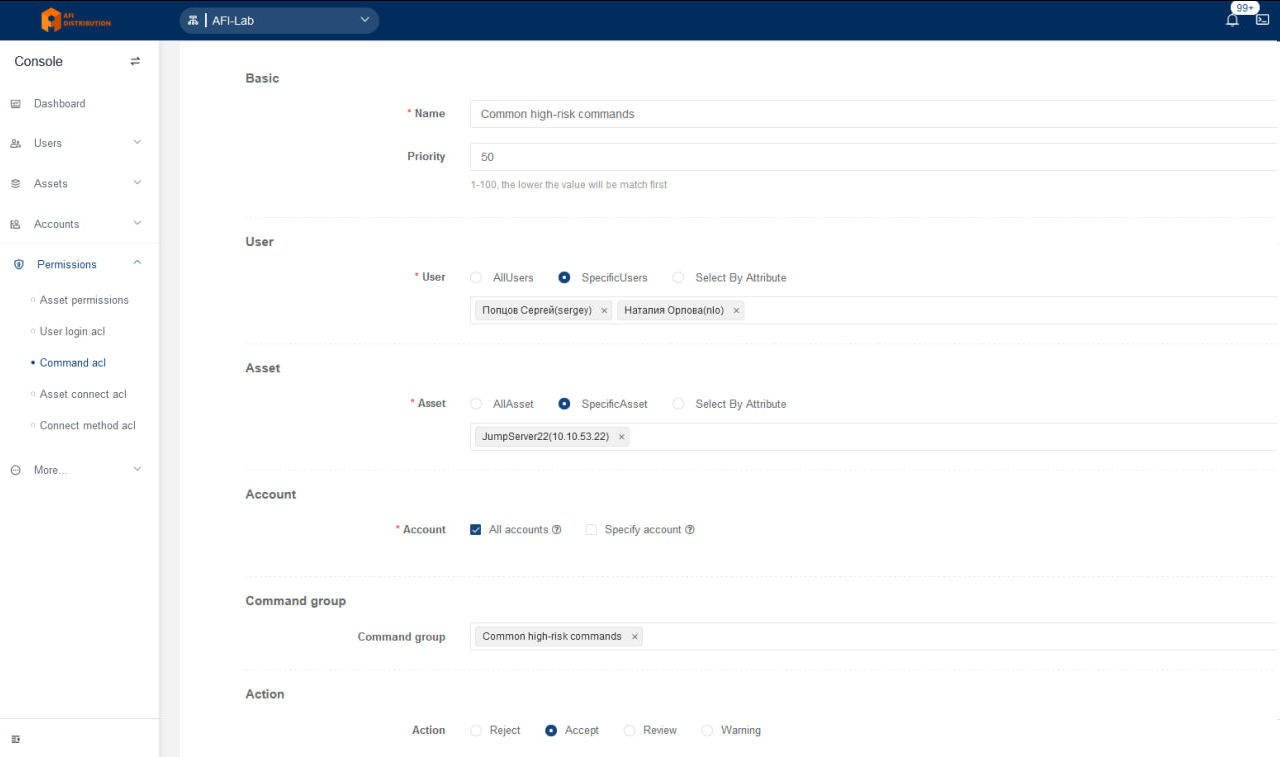
5. Click "Submit" to save the settings.
| << How to configure access to asset web-interface, HTTP session configuration | How to connect to domain assets using a single domain account? >> |
Stuck? If you are running a pilot, write to support@afi-d.com or in your project's Telegram group. Community Edition users can buy a support subscription: see Technical support. Video guides are on our YouTube channel.